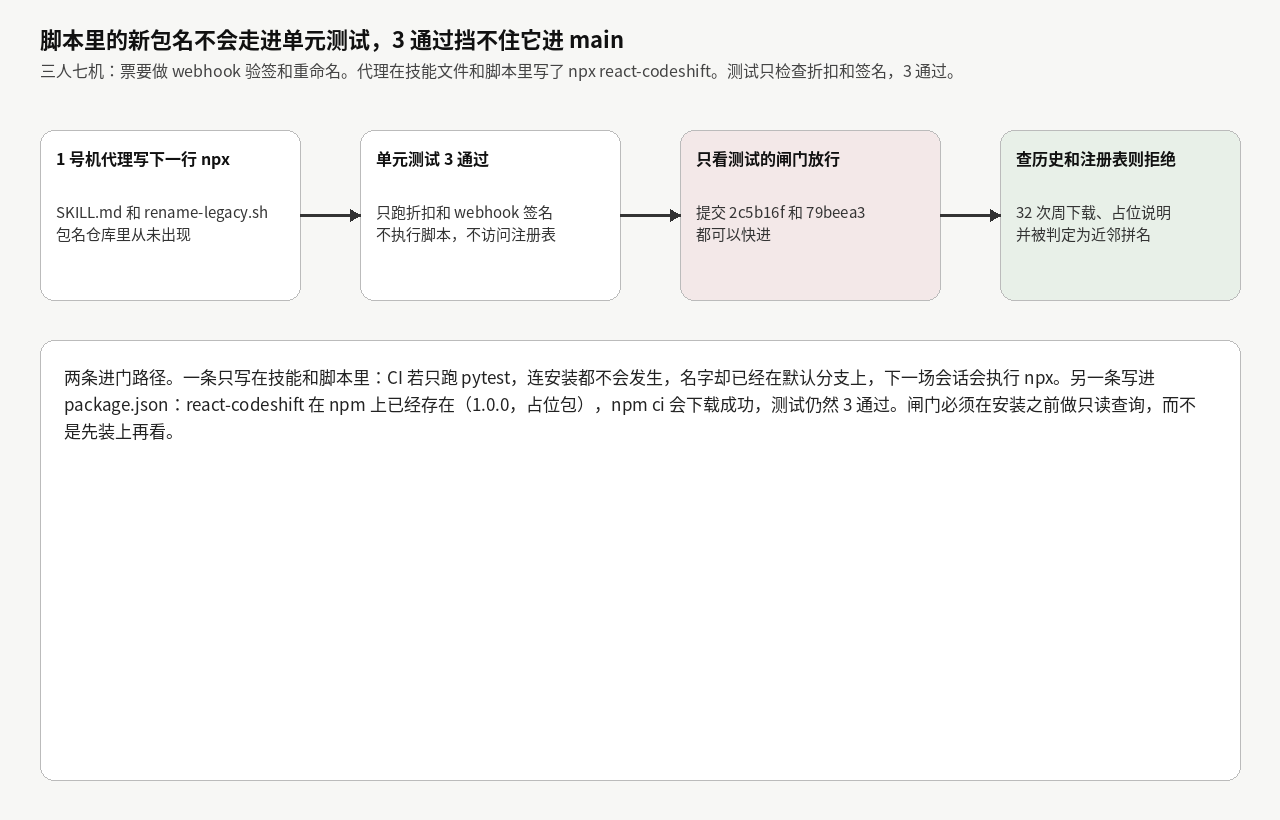
三人、七台电脑。1 到 3 号机跑编码代理,4、5 号机审查,6 号机做 Windows 验证,7 号机负责合入。这周的票有两件活:给账单服务的支付回调加上签名校验,以及把 apply_discount 重命名为 apply_discount_v2。签名校验用标准库里的 hmac 就能做,并不需要新依赖。1 号机的代理隔夜开工。周一早上,PR 已经开着,单元测试 3 通过。
多出来的不是函数,是两份说明书。一份在 .agents/skills/rename-discount/SKILL.md,一份在 tools/rename-legacy.sh。两处都是同一行:
npx react-codeshift --transform=react-codeshift/transforms/rename-apply-discount.js ./react-codeshift 这个名字,在这个仓库的历史上从未出现过。单元测试没有运行这行命令。它们只检查折扣计算和 webhook 签名,结果是 3 通过。如果 7 号机只看测试,这个名字会跟着进 main。下一场代理会话,或者下一位按技能文件操作的人,会在 1 号机上执行 npx。本地没有这个包时,npx 会去注册表取。
这篇要核对的是:一个仓库里从未出现过的包名,写在脚本、技能文件或 package.json 里,会不会被「测试全绿」放行;注册表上查到这个名字,是否就等于它安全;以及 7 号机在安装之前,究竟该查什么。它和 你装进 agent 的配置,是一条没有 lockfile 的供应链 谈的是代理自己的配置文件,和 你复制的 Skill,永远等不到补丁 谈的是技能文件复制之后得不到上游修复,和 两个代理同时加依赖,package-lock.json 冲突了 谈的是锁文件怎么合并,都不是同一件事。今天只谈:这个包名仓库里从未出现过,测试却已经是绿的。
我按常见的代理写法准备了这些提交,并没有在实验室里再开一个编码模型来生成它们。玩具仓库的 seed 是 908d7f0:一份用 hmac 校验 webhook 的账单服务,加上一个只声明了 express@4.21.2 的 package.json。我对 npm 和 PyPI 做了只读查询,没有安装、也没有执行任何一个新包。Windows 没有参与这次实验。
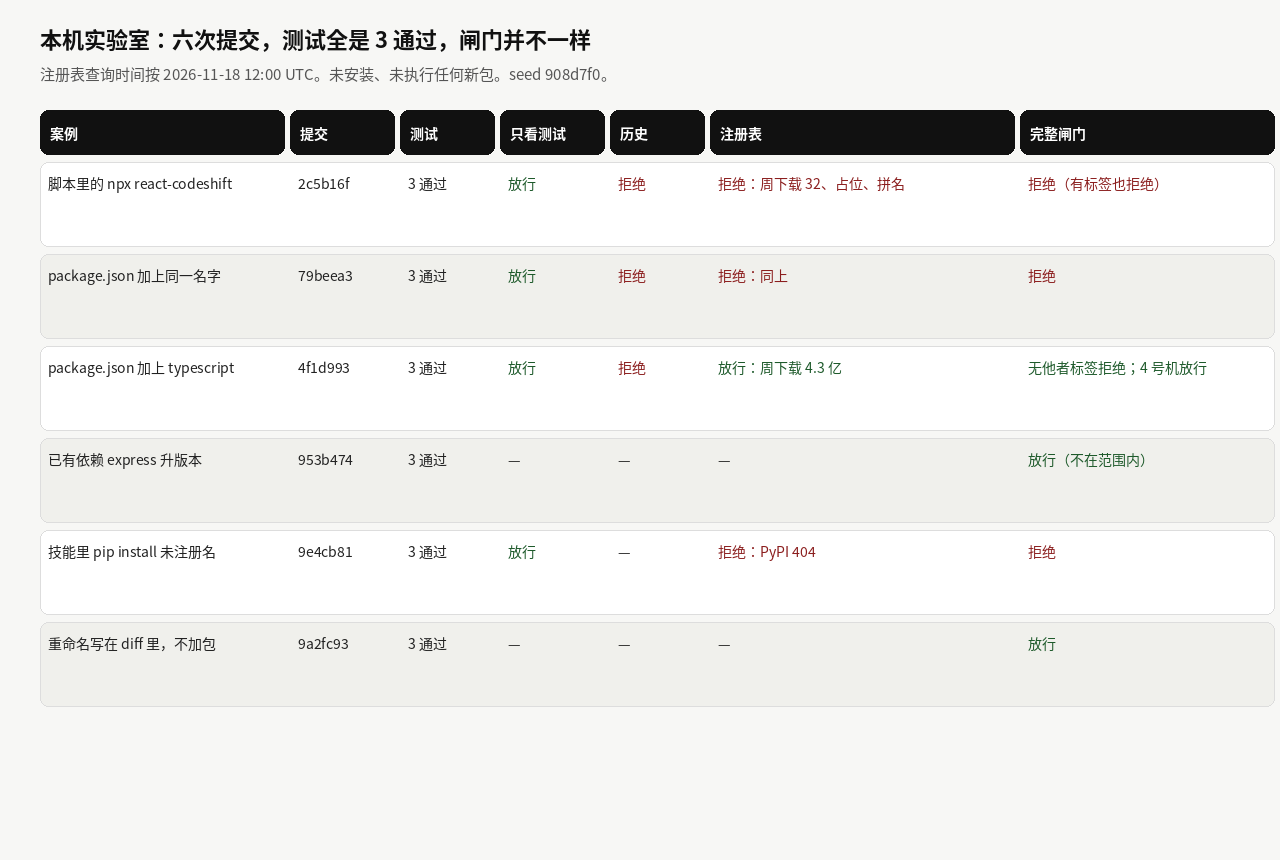
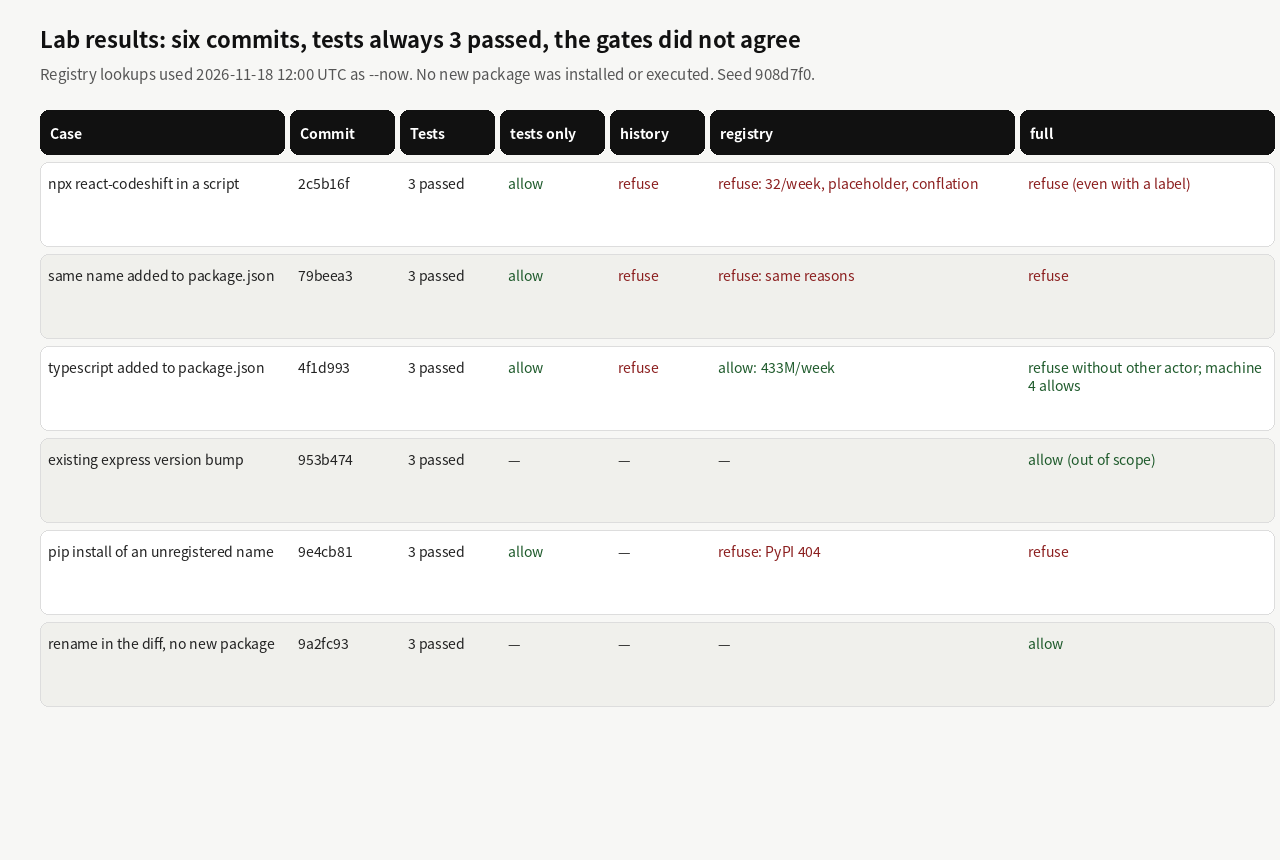
实验室里,六次提交的测试都是 3 通过
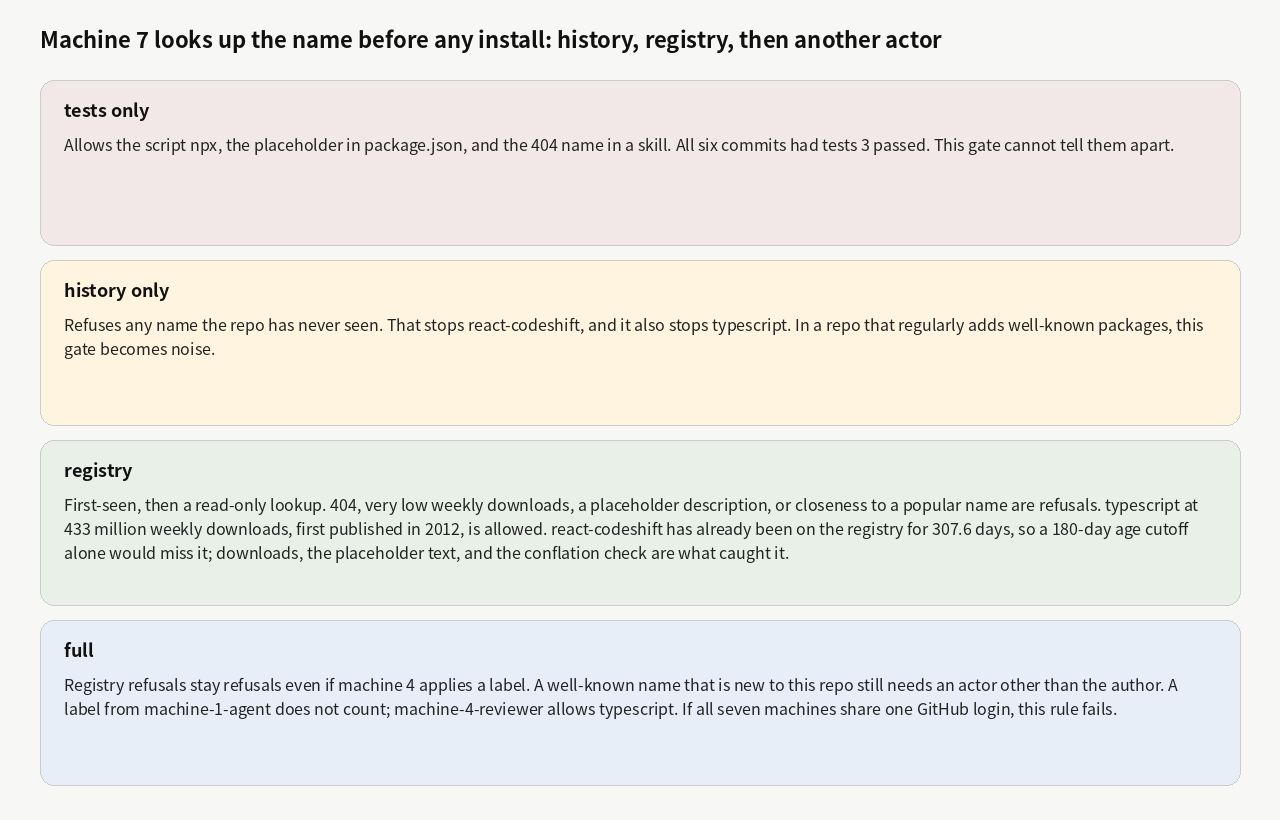
先说那份只写在技能和脚本里的 PR,提交是 2c5b16f。pytest 的结果是 3 passed。把闸门设成 tests_only,它放行,退出码 0。换成 history,它拒绝:react-codeshift 在 seed 的扫描范围内从未出现。再换成 registry,它仍然拒绝,但理由已经不是「没见过」这么简单。
2026-11-18 12:00 UTC 这一刻,我向 registry.npmjs.org/react-codeshift 做了查询。这个名字在注册表上是存在的。最新版本 1.0.0,创建时间 2026-01-14T21:02:51.762Z,距查询时刻 307.6 天。周下载 32 次。描述原文是:“Placeholder to prevent dependency confusion.”闸门因此给出三条风险理由:周下载低于 1000、说明写成占位、以及被判定为与 react、react-codemod、react-dom 的拼名。注意:单靠「发布不足 180 天」这一条,已经拦不住它了——它在注册表上待了十个月。npm view react-codeshift 的只读结果与这次查询一致。我没有运行 npm install 或 npx。
这个发现改变了「名字不存在就不会被装上」的直觉。写进技能文件的那条路径里,CI 若只跑 pytest,安装不会发生,名字却已经在默认分支上,下一场会话会执行 npx。我另做了一次提交 79beea3,把同一个名字写进 package.json 的 devDependencies,并加了一条 codemod 脚本。测试仍然 3 通过。因为这个名字在 npm 上已经存在,npm ci 会按 1.0.0 下载成功——今天下载到的是一个占位包,明天如果描述还是同一句话,并不保证内容仍是空的。闸门必须在安装之前做只读查询,而不是先装上再看。
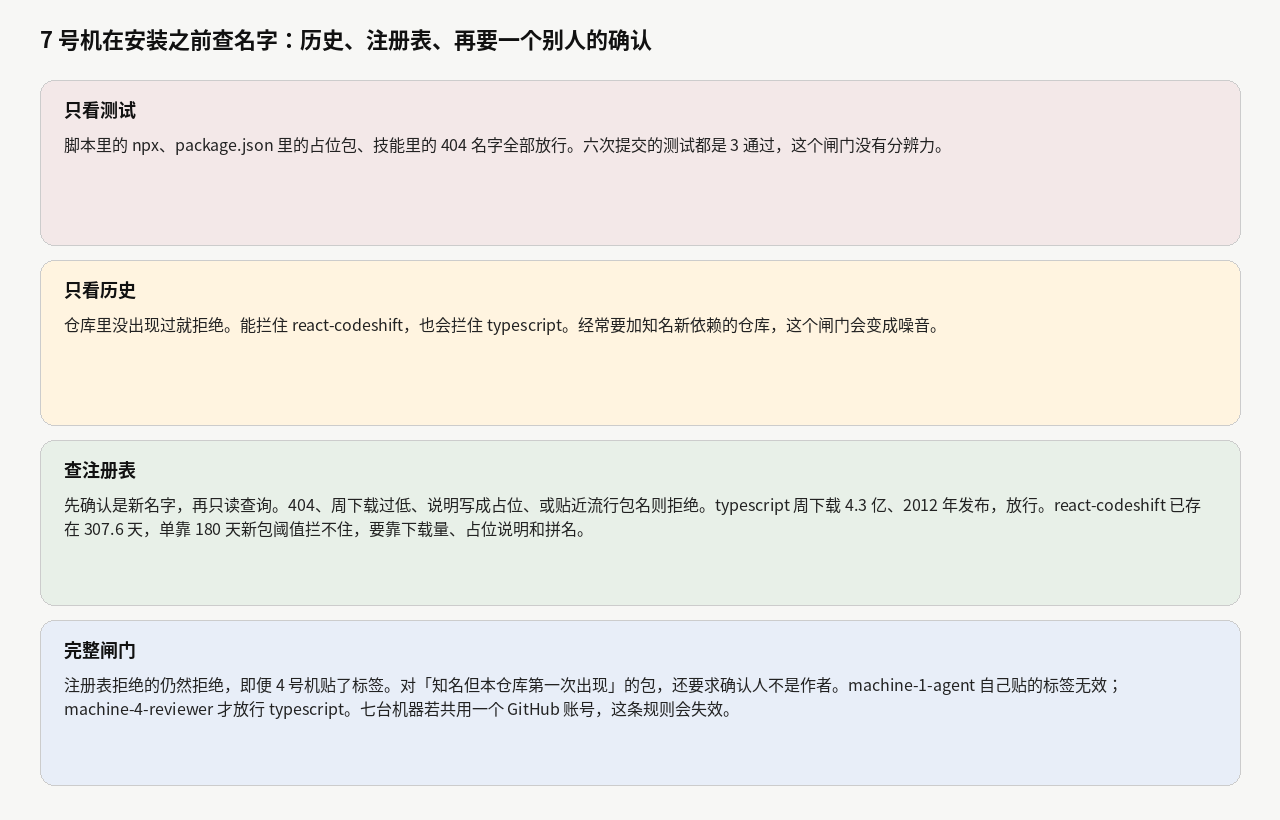
第三份 PR 用来对照。提交 4f1d993 只在 package.json 里加入了 typescript@5.6.3。测试同样 3 通过。history 拒绝它,因为它也是本仓库第一次出现。registry 放行:创建时间 2012-10-01T15:35:39.553Z,周下载 433,588,805。完整闸门在作者是 machine-1-agent、没有其他人确认时拒绝;把确认人写成同一个 machine-1-agent,仍然拒绝;写成 machine-4-reviewer,才放行。也就是说,知名包可以进仓库,但第一次出现仍然是一次需要人点头的变更,而且点头的不能是作者自己。
第四份提交 953b474 把已经在仓库里的 express 从 4.21.2 升到 4.22.0。完整闸门放行。这是有意的范围限制:这次闸门管的是「新名字」,不管「旧名字的新版本」。版本升级要另做漏洞扫描,不能把它当成已经检查过。
第五份提交 9e4cb81 在技能文件里写了 pip install stripe-webhooks-verify。这是我按「支付渠道名 + webhook + verify」拼出来的名字,用来模拟代理惯用的那种听起来很合理的组合。测试 3 通过。tests_only 放行。向 pypi.org/pypi/stripe-webhooks-verify/json 查询,HTTP 状态码是 404。registry 和完整闸门都拒绝,理由是 not_on_registry。名字今天不在注册表上,不等于它明天也不会在。一旦有人注册,下一场执行 pip install 的会话就会装上它。所以拒绝的原因不是「现在装不上」,而是「这个名字不该未经审查就写进仓库」。
第六份提交 9a2fc93 把重命名直接写进 billing.py 的 diff,加了一个 apply_discount_v2 别名,没有引入任何新包名。测试 3 通过,完整闸门放行。票面上的重命名,本来就可以这样交。
还要补一句:只靠 package.json 的 CODEOWNERS 也还不够。提交 2c5b16f 和 9e4cb81 都没有改 package.json,它们只改了技能文件和脚本。如果审查规则只盯着清单文件,这两条路径会从旁边走过去。闸门必须把安装命令从技能、shell、工作流和 Makefile 里扫出来,不能只 diff 依赖清单。
4 号机在审查时最容易看到的是测试摘要和 PR 标题。测试摘要会写 3 passed。标题可能会写完成了重命名。技能文件里的那一行 npx,除非有人把 diff 翻到 .agents/ 下面,否则不会进入审查视野。三人七机的节奏里,隔夜 PR 的 diff 往往比人愿意读的更长,而安装命令又常常藏在看起来像文档的 Markdown 里。
机制:测试看不见的名字,注册表存在也不等于可以信
单元测试在问一个问题:折扣算得对不对,伪造的 webhook 能不能改余额。它们不会打开 SKILL.md,不会跑 tools/rename-legacy.sh,也不会去问 npm 这个名字是什么。所以「3 通过」和「脚本里多了一个仓库从未出现过的包名」可以同时成立。这不是测试写错了,是它的职责本来就不包括这件事。
技能文件看起来像文档,对编码代理来说却是可执行说明。下一场会话会按里面的命令去做。npx 在本地找不到包时,默认会向注册表请求安装。把安装命令只写在 CI 不会跑到的路径里,并不能减小风险,只会把执行推迟到某一台开发机上。4 号机如果只读测试结果和 PR 标题,会觉得重命名已经准备好了。真正的命令可能要到合并之后,才第一次被执行。
注册表上查到这个名字,也不能当成安全证明。react-codeshift 在我查询的这一刻是存在的。它的说明写着自己是占位包,周下载只有 32 次,创建于 2026-01-14。这个日期和 Charlie Eriksen 在 Aikido 的公开说明一致:他在 2026 年 1 月 14 日抢注了这个名字,当时已有大量 GitHub 仓库在技能文件里引用它,来源可以追溯到 2025-10-17 wshobson/agents 的提交 65e5cb0。我没有重新统计那些仓库的数量,也没有复现当时的下载曲线。我核实的是今天的注册表记录:它仍然叫这个名字,版本 1.0.0,说明仍是占位,周下载 32。名字本身是 jscodeshift 和 react-codemod 的拼合,听起来像一个本该存在的工具。闸门里的拼名启发式给出了 react、react-codemod、react-dom——最后一项是误伤,因为比较表里带 react 这个词根的包不止一个。启发式会有假阳性,不能单独拿它当定罪证据;它只是让审查者把目光放到这个名字上。
还有一条容易被忽略的缝:用「发布不满 N 天」当唯一规则。react-codeshift 到查询时刻已经 307.6 天,180 天的新包阈值已经失效。拦下它的是周下载、占位说明和拼名。年龄会过期,下载量和说明未必会。
我没有把「先在 CI 里跑一遍技能,看看 npx 能不能用」当成修复。那会在闸门里执行这个包。只读查询的意义就在于:判断发生在安装之前。
什么时候不该装这套闸门
不要把 history 当成唯一规则,然后抱怨每次加入 typescript 都被拦住。经常要引入知名新依赖的仓库,应当用注册表模式处理风险名字,再用完整闸门或 CODEOWNERS,让人确认第一次出现的知名包。反过来,如果三人小团队几乎不加依赖,一份允许名单其实更干净:任何新名字都要人批准。那就是 history 模式,加上一份需要人维护的名单。实验室里 typescript 被 history 拒绝,正是这个选择的代价。
不要只拿包龄做决定。占位包在注册表上待十个月以后,仍然可以是一个不该自动放行的名字。
不要在七台机器共用一个 GitHub 账号的时候,指望 deps-ok 标签能区分作者和审查者。实验室里,确认人写成 machine-1-agent 自己,完整闸门对 typescript 仍然拒绝;写成 machine-4-reviewer 才放行。身份若是同一个登录,这条规则不是变严,是失效。审查机需要独立的身份,或者把 package.json、requirements.txt 和 .agents/ 交给 CODEOWNERS 里另一个人。
也不要把「给 1 到 3 号机断掉 npm 的外网」当成可以替代闸门的理由。这是一层很好的执行控制,能挡住开发机上当场的 npx。它挡不住名字先写进仓库,再在有网的 CI 或另一台电脑上被执行。两层要一起用。
不要以为这次闸门已经覆盖了依赖安全的全部问题。express 从 4.21.2 升到 4.22.0 被放行,是因为名字不是新的。版本升级、已知漏洞、安装脚本里的行为,要另做扫描。这次脚本也不查询私有源;只用了 npm 和 PyPI 的公开接口。公司内部包会表现为 404 或完全不同的元数据,需要改查询入口,而不是把公网 404 直接当成拒绝理由。
拼名启发式会误伤,也会漏。react-dom 被列进了接近列表;距离大于 2、或流行包不在那份短表里的名字,则可能漏掉。它是提示,不是证明。
明天能抄走的做法
在 1 到 3 号机的 AGENTS.md 里写清楚:仓库里从未出现过的包名、npx、npm install、pip install,不要和功能改动放在同一份 PR 里,除非审查已经同意这个名字。能在 diff 里完成的重命名,就不要再加一个安装命令。账单验签已经有 hmac,不要为此再加一个包。
在 7 号机合并之前,对 base..head 跑 check_new_packages.py 的 registry 模式。它会扫描 package.json、依赖清单,以及脚本、工作流、Makefile、技能文件里的安装命令。404、周下载过低、说明写成占位、或贴近流行包名的,直接拒绝。第一次引入的知名包,再用完整闸门或 CODEOWNERS,要求作者以外的人确认。不要用「先安装看看」来代替查询。
合并之后,如果 main 上新出现了一个安装命令,默认不要在开发机上执行它。先看注册表记录,再决定要不要装。
脚本、一份样例工作流和 AGENTS.md 片段在 first-seen-package-kit.tar.gz。这样调用:
python3 tools/check_new_packages.py --repo . --base <default-branch-sha> --head HEAD --mode registry
python3 tools/check_new_packages.py --repo . --base <default-branch-sha> --head HEAD --mode full --author machine-1-agent --deps-ok-actor machine-4-reviewer
样例工作流只检查了结构,没有在 GitHub Actions 上运行。
今天最小的一步:对即将合并的代理 PR,搜索 package.json、锁文件、技能文件和脚本里新出现的包名。凡是仓库历史里没有的,先向注册表做一次只读查询,再决定是否合并。不要用单元测试的绿来代替这次查询。
实际跑过什么
运行环境:本机 git 2.47.3、Python 3.13.5、pytest 9.1.1、Node.js 22.23.2、npm 11.21.1。查询时刻的 --now 为 2026-11-18T12:00:00Z。seed 908d7f0。脚本路径提交 2c5b16f:测试 3 通过,tests_only 放行,history / registry / 完整闸门(含 4 号机标签)均拒绝 react-codeshift;注册表存在,创建于 2026-01-14T21:02:51.762Z,年龄 307.6 天,周下载 32,说明为占位,拼名命中 react,react-codemod,react-dom。package.json 提交 79beea3:测试 3 通过,闸门结论相同。typescript 提交 4f1d993:测试 3 通过,history 拒绝,registry 放行(周下载 433,588,805,创建于 2012-10-01T15:35:39.553Z,年龄 5160.9 天),完整闸门在无确认人或确认人是作者时拒绝,确认人为 machine-4-reviewer 时放行。express 升级提交 953b474:测试 3 通过,完整闸门放行。技能里的 stripe-webhooks-verify 提交 9e4cb81:测试 3 通过,PyPI HTTP 404,registry 与完整闸门拒绝。只改 diff 的提交 9a2fc93:测试 3 通过,完整闸门放行。另用 npm view react-codeshift 核对名称、版本、说明和创建时间,与注册表查询一致。
未运行:npm install、npx、pip install 任何新包;GitHub Actions(YAML 只检查了结构);分支保护或 ruleset;第二个 GitHub 账号去贴真实的 deps-ok 标签;任何 Windows 作业或 windows-latest 运行器;私有 npm / PyPI 源;对 express 新版本做漏洞扫描。本地短哈希在固定时间戳重建下是稳定的。周下载 32 和 433,588,805 是这次查询当时的公开计数,会随时间变化。
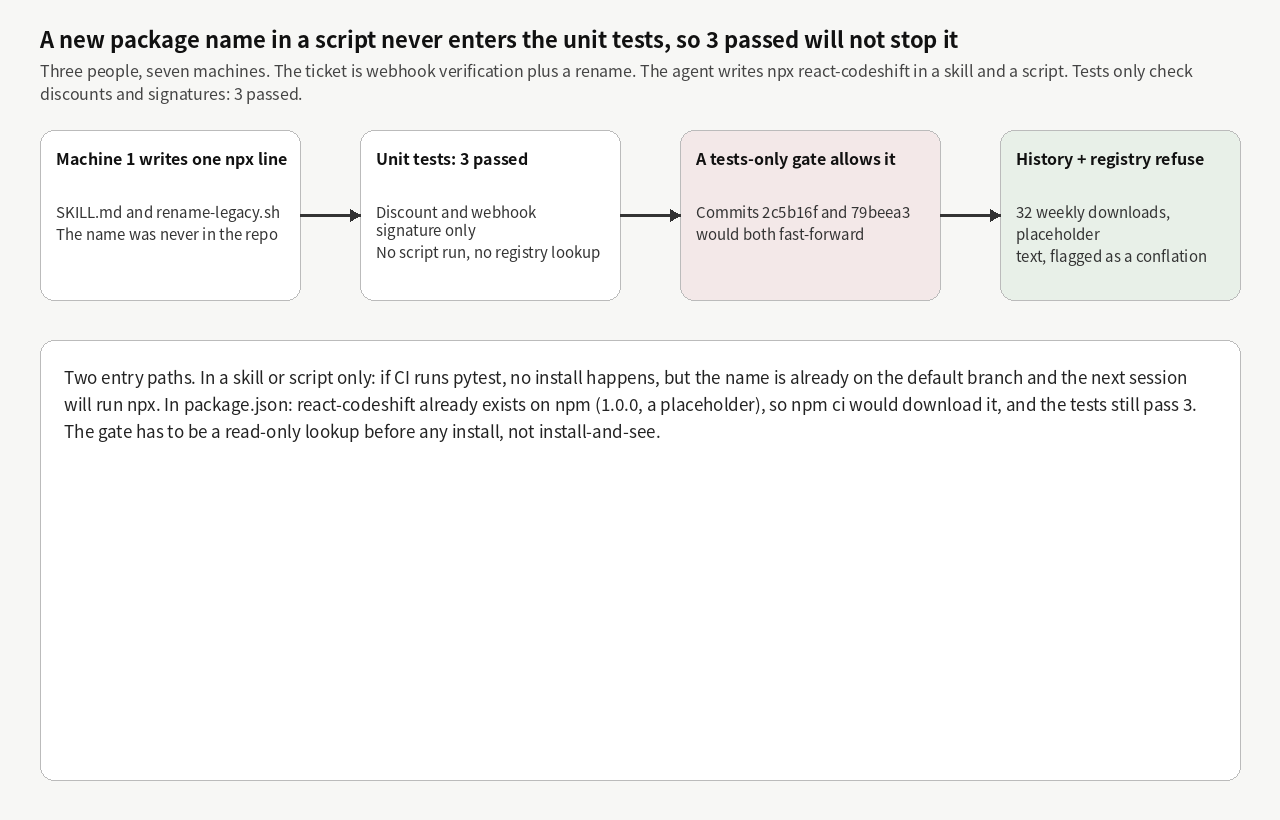
Three people, seven computers. Machines 1 to 3 run coding agents, 4 and 5 review, 6 does Windows validation, and 7 merges. This week's ticket has two jobs: verify signatures on the billing service's payment webhooks, and rename apply_discount to apply_discount_v2. The signature check can be done with hmac in the standard library. It does not need a new dependency. The agent on machine 1 starts overnight. On Monday morning the PR is open, and the unit tests have 3 passed.
What appeared in the PR is not a new function. It is two instruction files. One lives at .agents/skills/rename-discount/SKILL.md, the other at tools/rename-legacy.sh. Both contain the same line:
npx react-codeshift --transform=react-codeshift/transforms/rename-apply-discount.js ./The name react-codeshift has never appeared in this repository. The unit tests did not run that command. They only check discount arithmetic and webhook signatures, and the result is 3 passed. If machine 7 looks only at the tests, the name lands on main. The next agent session, or the next person who follows the skill file, will run npx on machine 1. If the package is not present locally, npx will fetch it from the registry.
This post asks three questions. If a package name that has never appeared in the repo is written into a script, a skill file, or package.json, will “tests are green” let it through? If the name exists on the registry, does that make it safe? And what should machine 7 look up before any install happens? This is not the same as your agent config has no lockfile, which is about the agent's own configuration files; or the skill you copied never gets the patch, which is about copied skill files missing upstream fixes; or two agents adding dependencies at once and conflicting in package-lock.json, which is about merging lockfiles. Today is only this: the package name has never been in the repo, and the tests are already green.
I prepared these commits in the usual shape of an agent change. I did not open a coding model in the lab to generate them. The toy repository seed is 908d7f0: a billing service that verifies webhooks with hmac, plus a package.json that only declares express@4.21.2. I made read-only queries to npm and PyPI. I did not install or execute any new package. Windows did not take part in this experiment.
In the lab, all six commits had tests 3 passed
Start with the PR that only adds a skill and a script. The commit is 2c5b16f. pytest reported 3 passed. With the gate set to tests_only, it allowed the merge, exit code 0. In history mode it refused: react-codeshift had never appeared in the seed's scanned files. In registry mode it still refused, for reasons that go beyond “we have not seen this name.”
At 2026-11-18 12:00 UTC I queried registry.npmjs.org/react-codeshift. The name exists on the registry. The latest version is 1.0.0. It was created at 2026-01-14T21:02:51.762Z, 307.6 days before the query. Weekly downloads were 32. The description is: “Placeholder to prevent dependency confusion.” The gate therefore recorded three risk reasons: weekly downloads below 1,000, a placeholder description, and a conflation with react, react-codemod, and react-dom. A rule that only rejects packages younger than 180 days would already have missed it — the name has been on the registry for ten months. A read-only npm view react-codeshift agreed with this query. I did not run npm install or npx.
That result undercuts the intuition that “if the name does not exist, it cannot be installed.” On the skill-file path, if CI only runs pytest, no install happens, but the name is already on the default branch, and the next session will run npx. I made a second commit, 79beea3, that adds the same name to devDependencies in package.json and a codemod script. The tests still passed 3. Because the name already exists on npm, npm ci would download version 1.0.0 successfully. What you would get today is a placeholder package. If the description is still the same sentence tomorrow, that does not guarantee the contents are still empty. The gate has to be a read-only lookup before any install, not install-and-see.
The third PR is a contrast. Commit 4f1d993 only adds typescript@5.6.3 to package.json. The tests again passed 3. history refused it, because this repo had never seen the name either. registry allowed it: created at 2012-10-01T15:35:39.553Z, weekly downloads 433,588,805. The full gate refused when the author was machine-1-agent and nobody else had confirmed; it still refused when the confirming actor was the same machine-1-agent; it allowed only when the confirming actor was machine-4-reviewer. A well-known package can enter the repo, but the first time it appears is still a change that needs a person, and that person cannot be the author.
The fourth commit, 953b474, bumps the existing express dependency from 4.21.2 to 4.22.0. The full gate allowed it. That is a deliberate limit of scope: this gate is about new names, not new versions of old names. Version bumps need a separate advisory scan. Do not treat them as already checked.
The fifth commit, 9e4cb81, puts pip install stripe-webhooks-verify in a skill file. I coined that name by joining a payment-provider token with webhook and verify, the kind of plausible blend an agent often writes. The tests passed 3. tests_only allowed it. A query to pypi.org/pypi/stripe-webhooks-verify/json returned HTTP 404. Both registry and the full gate refused, with the reason not_on_registry. A name that is unregistered today may be registered tomorrow. The next session that runs pip install would then install it. The refusal is not “it cannot be installed right now.” It is “this name should not enter the repository without a review.”
The sixth commit, 9a2fc93, does the rename in the billing.py diff itself, by adding an apply_discount_v2 alias, and introduces no new package name. The tests passed 3, and the full gate allowed it. That is how the rename on the ticket could have been delivered.
One more gap: CODEOWNERS on package.json is not enough on its own. Commits 2c5b16f and 9e4cb81 do not touch package.json. They only change a skill file and a script. If the review rule only watches the manifest, both paths walk around it. The gate has to extract install commands from skills, shell scripts, workflows, and Makefiles. Diffing the dependency manifest is not sufficient.
What machine 4 is most likely to see in review is the test summary and the PR title. The summary will say 3 passed. The title may say the rename is done. The npx line in the skill file will not enter the review at all unless someone scrolls the diff into .agents/. On a three-person, seven-machine cadence, an overnight PR is often longer than a person wants to read, and the install command is often hidden in Markdown that looks like documentation.
The mechanism: tests cannot see the name, and a registry hit is not a safety proof
The unit tests ask one question: is the discount arithmetic right, and can a forged webhook change the balance? They do not open SKILL.md, they do not run tools/rename-legacy.sh, and they do not ask npm what the name is. So “3 passed” and “a script now contains a package name the repo has never seen” can be true at the same time. That is not a bug in the tests. It is not their job.
A skill file looks like documentation. For a coding agent it is an executable instruction. The next session will follow the commands in it. When npx cannot find the package locally, it will typically ask the registry to install it. Putting the install command only on a path CI does not run does not shrink the risk. It defers execution to some development machine. If machine 4 only reads the test results and the PR title, the rename looks ready. The command itself may be executed for the first time after the merge.
Finding the name on the registry is not a safety proof either. react-codeshift existed at the moment I queried it. Its description calls it a placeholder, weekly downloads were 32, and it was created on 2026-01-14. That date matches Charlie Eriksen's public account at Aikido: he reserved the name on 14 January 2026, when a large number of GitHub repositories already mentioned it in skill files, tracing back to commit 65e5cb0 in wshobson/agents on 2025-10-17. I did not recount those repositories, and I did not reproduce the download curve from that period. What I verified is today's registry record: the name is still there, version 1.0.0, the description is still a placeholder, weekly downloads 32. The name itself is a blend of jscodeshift and react-codemod, and it sounds like a tool that ought to exist. The gate's conflation heuristic reported react, react-codemod, and react-dom — the last of these is a false hit, because more than one package in the comparison set carries the react token. Heuristics produce false positives. They are not a verdict on their own. They are there to point a reviewer at the name.
There is another seam that is easy to miss: using “published less than N days ago” as the only rule. At query time react-codeshift was already 307.6 days old, so a 180-day cutoff had expired. What still caught it were the weekly downloads, the placeholder description, and the conflation check. Age expires. Download counts and descriptions may not.
I did not treat “run the skill in CI and see whether npx works” as the fix. That would execute the package inside the gate. The point of a read-only lookup is that the decision happens before any install.
When you should not install this
Do not make history the only rule and then complain that adding typescript is blocked every time. A repository that regularly takes on well-known new dependencies should use registry mode for risky names, and then the full gate or CODEOWNERS so a person confirms a well-known name on its first appearance. Conversely, if a three-person team almost never adds dependencies, an allowlist is cleaner: every new name needs a person. That is history mode, plus a list someone has to maintain. In the lab, history refusing typescript is exactly the cost of that choice.
Do not decide on package age alone. A placeholder can sit on the registry for ten months and still be a name that should not be auto-merged.
Do not expect a deps-ok label to tell the author from the reviewer when all seven machines share one GitHub login. In the lab, setting the confirming actor to machine-1-agent itself still refused typescript; machine-4-reviewer was what allowed it. If the identity is the same login, the rule does not get stricter. It fails. The review machine needs a distinct identity, or package.json, requirements.txt, and .agents/ need a different person in CODEOWNERS.
Do not treat “cut npm's network access on machines 1 to 3” as a substitute for the gate. That is a good execution control. It can stop a live npx on a development machine. It cannot stop the name being written into the repository and later executed on a networked CI job or another computer. Use both.
Do not assume this gate covers the rest of dependency safety. express 4.21.2 to 4.22.0 was allowed because the name was not new. Version bumps, known advisories, and install-script behavior need a separate scan. This script also does not query private registries; it only uses the public npm and PyPI APIs. An internal package will look like a 404, or like entirely different metadata. Change the lookup endpoint. Do not treat a public 404 as an automatic refusal in that case.
The conflation heuristic will both over-fire and miss. react-dom was listed as a neighbor; a name whose edit distance is greater than 2, or whose popular neighbor is not in the short list, can slip through. It is a hint, not a proof.
What to copy tomorrow
In AGENTS.md for machines 1 to 3, say this plainly: a package name, an npx command, an npm install, or a pip install that has never appeared in this repository should not share a PR with a feature change unless a reviewer has already agreed to the name. If the rename can be done in the diff, do not add an install command. The billing webhook already has hmac. Do not add a package for it.
Before machine 7 merges, run check_new_packages.py in registry mode on base..head. It scans package.json, dependency manifests, and install commands in scripts, workflows, Makefiles, and skill files. A 404, very low weekly downloads, a placeholder description, or closeness to a popular name is a refusal. For a well-known package that is new to this repo, use the full gate or CODEOWNERS, and require a person other than the author. Do not replace the lookup with “install it and see.”
After the merge, if a new install command has appeared on main, do not run it on a development machine by default. Read the registry record first, then decide whether to install.
The scripts, a sample workflow, and the AGENTS.md snippet are in first-seen-package-kit.tar.gz. Call the gate like this:
python3 tools/check_new_packages.py --repo . --base <default-branch-sha> --head HEAD --mode registry
python3 tools/check_new_packages.py --repo . --base <default-branch-sha> --head HEAD --mode full --author machine-1-agent --deps-ok-actor machine-4-reviewer
The sample workflow YAML was checked for structure. It was not run on GitHub Actions.
The smallest step today: on an agent PR that is about to merge, search package.json, the lockfile, skill files, and scripts for package names that are new in the diff. If a name is not in the repository history, do a read-only registry lookup before you merge. Do not let a green unit-test job stand in for that lookup.
What was actually run
Runtime: git 2.47.3, Python 3.13.5, pytest 9.1.1, Node.js 22.23.2, and npm 11.21.1 on this machine. The --now value for age calculations was 2026-11-18T12:00:00Z. Seed 908d7f0. Script-path commit 2c5b16f: tests 3 passed; tests_only allowed; history, registry, and the full gate (including a machine-4 label) all refused react-codeshift; the package exists on the registry, created at 2026-01-14T21:02:51.762Z, age 307.6 days, weekly downloads 32, placeholder description, conflation hit react,react-codemod,react-dom. package.json commit 79beea3: tests 3 passed, same gate results. typescript commit 4f1d993: tests 3 passed; history refused; registry allowed (weekly downloads 433,588,805, created at 2012-10-01T15:35:39.553Z, age 5160.9 days); the full gate refused with no confirming actor or with the author as the confirming actor, and allowed when the confirming actor was machine-4-reviewer. express bump 953b474: tests 3 passed, full gate allowed. Skill-file stripe-webhooks-verify commit 9e4cb81: tests 3 passed, PyPI HTTP 404, registry and the full gate refused. Diff-only commit 9a2fc93: tests 3 passed, full gate allowed. A separate npm view react-codeshift confirmed the name, version, description, and created time, matching the registry query.
Not run: npm install, npx, or pip install of any new package; GitHub Actions (the YAML was checked for structure); branch protection or a ruleset; a second GitHub account to apply a real deps-ok label; any Windows job or windows-latest runner; a private npm or PyPI registry; an advisory scan of the new express version. Local short hashes are stable in this fixed-timestamp rebuild. The weekly download counts of 32 and 433,588,805 are the public figures at the time of this query, and they will change.